Log Search
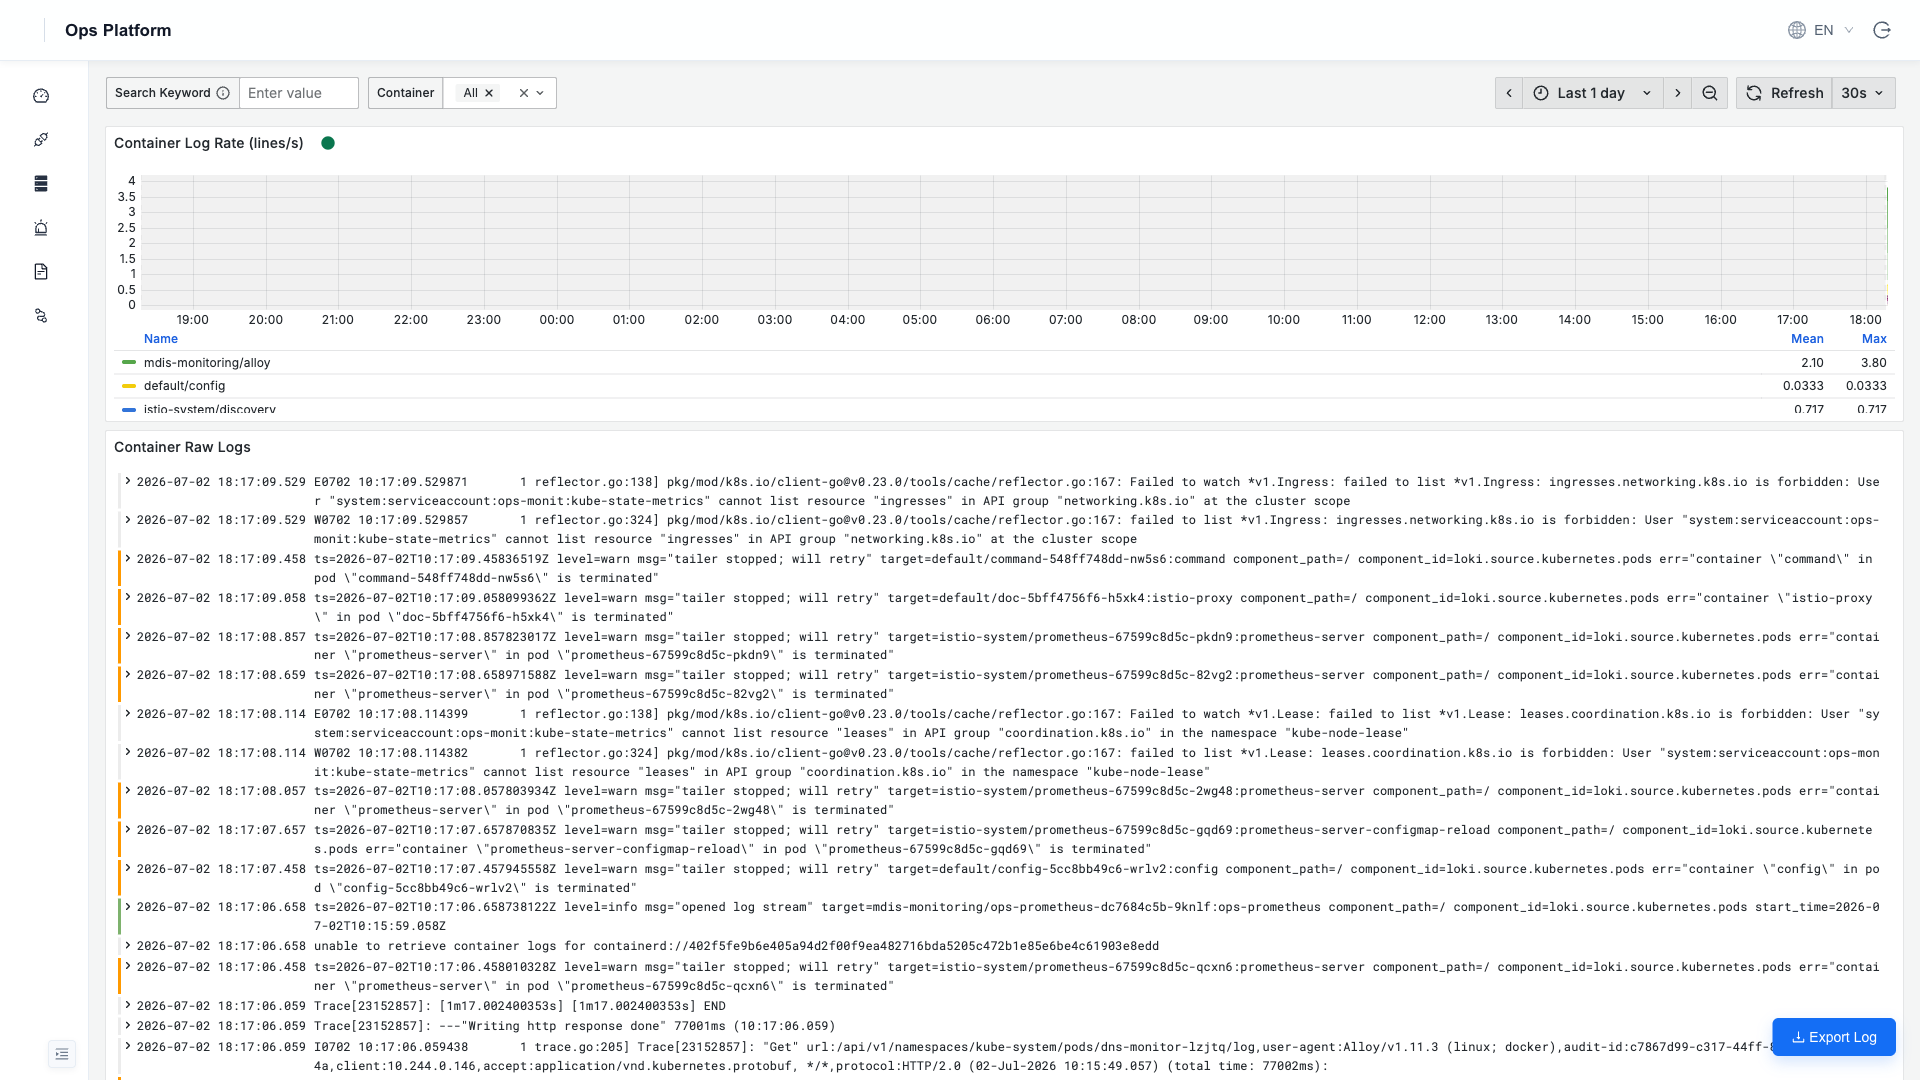
The Ops Platform uses Loki to query logs. The two panels under "Log Management" query logs from different sources:
| Panel | Source | Use Case |
|---|---|---|
| Container Console | Docker container or Kubernetes Pod stdout/stderr (collected by Alloy) | Troubleshoot middleware and infrastructure container logs, such as MySQL/Redis/Kafka |
| Service Logs | Structured JSON logs pushed directly by HAP/HDP microservices through serilog | Troubleshoot business calls, exception stacks, and search by parameters such as phone number/user ID/traceID |
Both panels support full-text keyword search and multi-select filters. Search is case-insensitive. Logs from the last 1 day are queried by default; adjust the time range in the upper-right corner.
Container Console
Select a container name (for example, script-app-1 or milvus-etcd) from the "Container" dropdown to view recent stdout for that container. Use keywords to locate specific content.
Service Logs
"Service Logs" queries structured logs pushed directly to Loki by HAP/HDP microservices through serilog.
Connect Service Logs
Service log writing must be enabled on the HAP/HDP service side. See Service Log Ingestion for configuration and verification steps.
Advanced LogQL
For aggregation, statistics, or regular expression matching, open Explore using the Grafana icon in the lower-left corner and query with LogQL:
{service_name="smssenderservice", detected_level="error"}     # All errors from the SMS service
{hostname=~".+"} |~ "(?i)13800138000"                          # Search a phone number across all microservices
sum(rate({hostname=~".+"}[5m])) by (service_name)              # 5-minute log rate by service
See the official LogQL documentation for syntax.
Logs are retained for 30 days by default (ENV_LOKI_RETENTION=720h). This can be adjusted in ops.yaml/ConfigMap. When disk capacity is limited, an S3/MinIO backend is recommended.